---
title: Kibana privileges
description: Kibana privileges grant users access to features within Kibana. Roles have privileges to determine whether users have write or read access. To learn how...
url: https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/deploy-manage/users-roles/cluster-or-deployment-auth/kibana-privileges
products:
- Elastic Documentation
- Kibana
applies_to:
- Elastic Stack: Generally available
---
# Kibana privileges
Kibana privileges grant users access to features within Kibana. Roles have privileges to determine whether users have write or read access.
To learn how to assign privileges to a role, refer to [Defining roles](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/deploy-manage/users-roles/cluster-or-deployment-auth/defining-roles).
## Base privileges
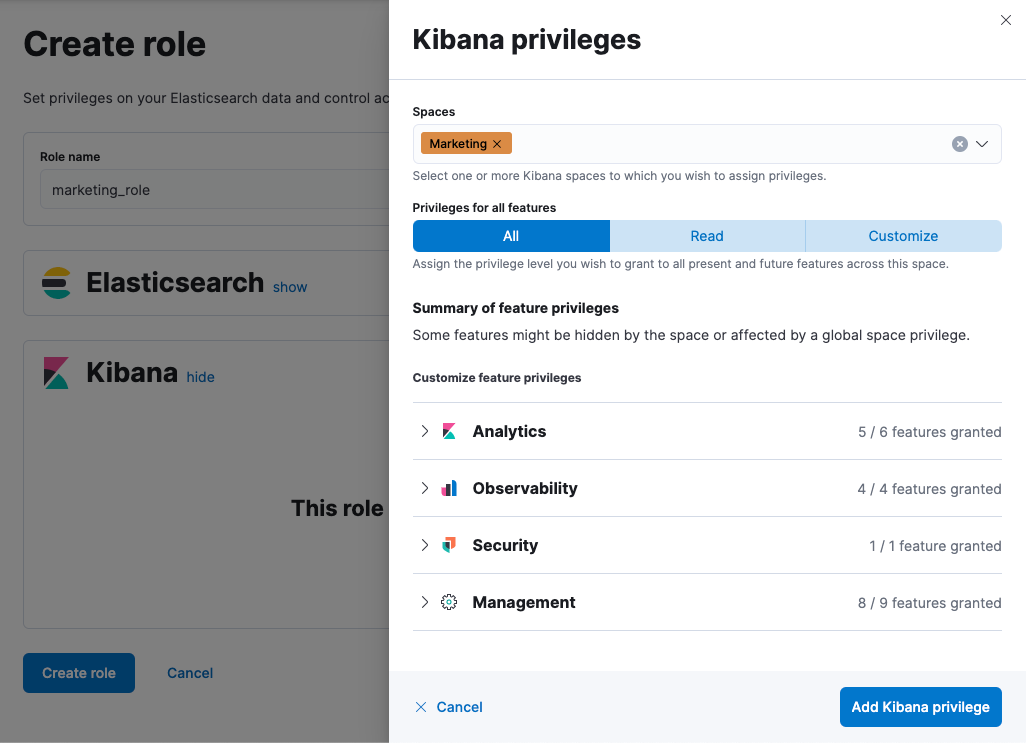
Assigning a base privilege applies the same access level across all feature groups instead of setting a level for each feature.
Some features and sub-feature privileges are excluded from base privileges and must be granted individually.
- **All**: Grants full read-write access.
- **Read**: Grants read-only access.
- **Customize**: Allows you to set the access level for each feature separately.
### Assigning base privileges
From the role management screen:
Using the [role APIs](https://www.elastic.co/docs/api/doc/kibana/group/endpoint-roles):
```js
PUT /api/security/role/my_kibana_role
{
"elasticsearch": {
"cluster" : [ ],
"indices" : [ ]
},
"kibana": [
{
"base": ["all"],
"feature": {},
"spaces": ["marketing"]
}
]
}
```
## Feature privileges
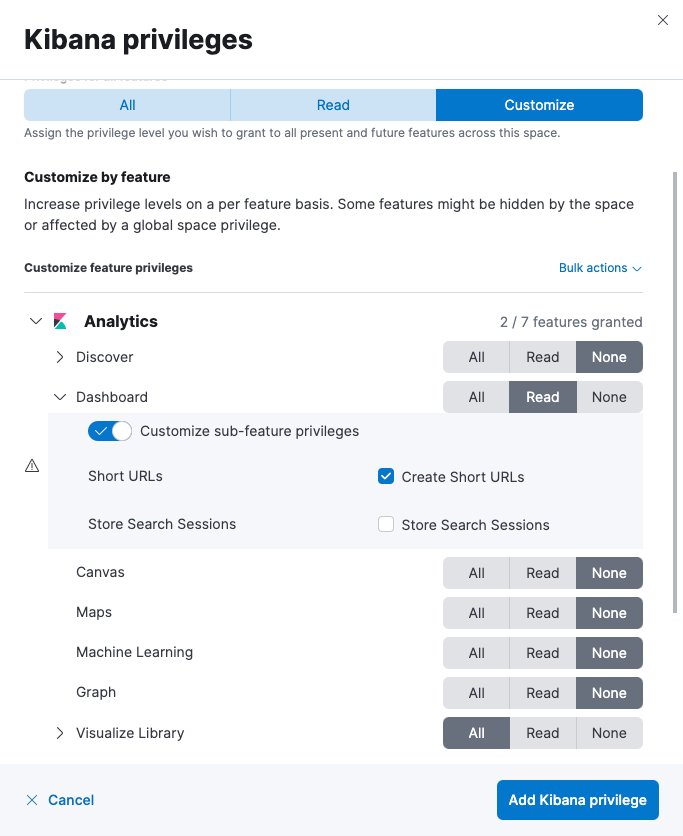
Assigning a feature privilege grants access to a specific feature. For each feature, select the type of access you want to allow:
- **All**: Users have full access to the feature, which includes performing all available actions and managing configuration.
- **Read**: Users can view the feature, but can't perform any actions or manage configuration.
- **None**: Users can't access or view the feature.
Some features don't have a **Read** privilege.
In role management, features are organized into the following groups.
| Group | What it contains |
|-----------------------------------------------------------------------------------------------------------------------------------------------|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Analytics** | Privileges for the features you use to explore and visualize data. Refer to [Privileges in the Analytics group](#kibana-privileges-analytics). |
| **Universal Alerting** Elastic Cloud Serverless: Generally available Elastic Stack: Planned | Privileges for Kibana Universal Alerting. Refer to [Configure access to Kibana Universal Alerting](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/explore-analyze/alerting/esql/manage/configure-access). |
| **Elasticsearch** | Privileges for Elasticsearch features. |
| **Observability** | Privileges for Elastic Observability features. Refer to [Observability Kibana privileges](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/solutions/observability/get-started/observability-kibana-privileges). |
| **Security** | Privileges for Elastic Security features. Refer to [Security Kibana privileges](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/solutions/security/manage/security-kibana-privileges). |
| **Management** | Privileges for the features you use to administer Kibana and your data. Refer to [Privileges in the Management group](#kibana-privileges-management). |
### Sub-feature privileges
Some features allow for finer access control than the **All** and **Read** privileges. This additional level of control is a [subscription feature](https://www.elastic.co/subscriptions).
### Assigning feature privileges
From the role management screen:
Using the [role APIs](https://www.elastic.co/docs/api/doc/kibana/group/endpoint-roles):
```js
PUT /api/security/role/my_kibana_role
{
"elasticsearch": {
"cluster" : [ ],
"indices" : [ ]
},
"kibana": [
{
"base": [],
"feature": {
"visualize_v2": ["all"],
"dashboard_v2": ["read", "url_create"]
},
"spaces": ["marketing"]
}
]
}
```
## Privileges in the Analytics group
Each of the following privileges controls access to a different feature.
| Privilege | What it allows |
|------------------------------------------------------------------------------------------------------------------------------------|-----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Discover** | Access [Discover](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/explore-analyze/discover), and save and manage Discover sessions. Turn on **Customize sub-feature privileges** to grant individual Discover privileges. For the full list, refer to [Discover sub-feature privileges](#kibana-privileges-discover-subfeatures). |
| **Dashboard** | Access [dashboards](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/explore-analyze/dashboards), and create and edit them. To add new visualizations or maps to a dashboard, users also need the **Visualize library** or **Maps** privilege. Turn on **Customize sub-feature privileges** to grant individual dashboard privileges. For the full list, refer to [Dashboard sub-feature privileges](#kibana-privileges-dashboard-subfeatures). |
| **Canvas** | Access [Canvas](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/explore-analyze/visualize/canvas), and create and edit workpads. Turn on **Customize sub-feature privileges** to grant the reporting privilege. For details, refer to [Canvas sub-feature privileges](#kibana-privileges-canvas-subfeatures). |
| **Maps** | Access [Maps](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/explore-analyze/visualize/maps), create and edit maps, and add maps to dashboards. |
| **Machine Learning** | Access [machine learning](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/explore-analyze/machine-learning), and create and manage jobs and trained models. This privilege grants the same access level to data views, dashboards, Discover sessions, and visualizations. |
| **Graph** | Access [Graph](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/explore-analyze/visualize/graph), and create and edit graphs. |
| **Visualize library** | Access the [Visualize library](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/explore-analyze/visualize), create and edit visualizations, and add visualizations to dashboards. Turn on **Customize sub-feature privileges** to grant individual Visualize library privileges. For the full list, refer to [Visualize library sub-feature privileges](#kibana-privileges-visualize-subfeatures). |
| **Agent Builder** Elastic Stack: Generally available since 9.2 | Access [Elastic Agent Builder](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/explore-analyze/ai-features/elastic-agent-builder), including agents, tools, and conversations. Elastic Stack: Generally available since 9.4 Turn on **Customize sub-feature privileges** to grant individual Elastic Agent Builder privileges. For the full list, refer to [Elastic Agent Builder permissions](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/explore-analyze/ai-features/agent-builder/permissions). |
| **Context Engine** Elastic Stack: Planned Elastic Cloud Serverless: Experimental | Access [Context Engine](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/explore-analyze/ai-features/context-engine). **Read** allows viewing AI indices and retrieving context. **All** also allows creating, editing, and deleting AI indices. Users need separate Elasticsearch index privileges to access backing indices and source data. |
| **Agent Builder - Semantic Metadata Layer (SML)** Elastic Stack: Generally available since 9.5 | Access the semantic metadata that Elastic Agent Builder uses to interpret your data. Elastic Stack: Generally available in 9.5 This privilege is called **Agent Context Layer**. |
| **Workflows** Elastic Stack: Generally available since 9.3 | Access [Workflows](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/explore-analyze/workflows), and create, edit, and run workflows. Turn on **Customize sub-feature privileges** to grant individual workflow privileges. For the full list, refer to [Workflows sub-feature privileges](#kibana-privileges-workflows-subfeatures). |
### Discover sub-feature privileges
These privileges control specific actions in Discover. Selecting **All** includes everything in the following table.
| Privilege | What it allows |
|-----------------------------|-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Create Short URLs** | Create short URLs for Discover sessions, so that they can be shared. |
| **Store Background search** | Save the results of a long-running search, so that they can be viewed again without rerunning the search. Elastic Stack: Generally available from 9.0 to 9.1 This privilege is called **Store Search Sessions**. |
| **Generate CSV reports** | Export the results of a Discover session as a CSV file. |
### Dashboard sub-feature privileges
These privileges control specific actions on dashboards. Selecting **All** includes everything in the following table.
| Privilege | What it allows |
|-------------------------------------------------------|-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Create Short URLs** | Create short URLs for dashboards, so that they can be shared. |
| **Store Background search** | Save the results of a long-running search, so that they can be viewed again without rerunning the search. Elastic Stack: Generally available from 9.0 to 9.1 This privilege is called **Store Search Sessions**. |
| **Generate PDF or PNG reports** | Export a dashboard as a PDF or PNG file. |
| **Generate CSV reports from Discover session panels** | Export the data behind a Discover session panel as a CSV file. |
### Canvas sub-feature privileges
This privilege controls a specific action in Canvas. Selecting **All** includes everything in the following table.
| Privilege | What it allows |
|--------------------------|---------------------------------|
| **Generate PDF reports** | Export a workpad as a PDF file. |
### Visualize library sub-feature privileges
These privileges control specific actions in the Visualize library. Selecting **All** includes everything in the following table.
| Privilege | What it allows |
|---------------------------------|-------------------------------------------------------------------|
| **Create Short URLs** | Create short URLs for visualizations, so that they can be shared. |
| **Generate PDF or PNG reports** | Export a visualization as a PDF or PNG file. |
### Workflows sub-feature privileges
- Elastic Stack: Generally available since 9.3
These privileges control specific actions on workflows. Selecting **All** includes every privilege in the following table except **Update managed workflows**, which you grant separately.
| Privilege | What it allows |
|-----------------------------------------------------------------------------------------------------------|---------------------------------------------------------|
| **Create** | Create workflows. |
| **Update** | Edit existing workflows. |
| **Delete** | Delete workflows. |
| **Execute** | Run workflows. |
| **Read** | View workflows. |
| **Read Workflow Execution** | View the results of a workflow run, including its logs. |
| **Cancel Workflow Execution** | Stop a workflow that's currently running. |
| **Read managed workflows** Elastic Stack: Generally available since 9.5 | View the workflows that Elastic provides. |
| **Read managed workflow execution** Elastic Stack: Generally available since 9.5 | View the results of a managed workflow run. |
| **Update managed workflows** Elastic Stack: Generally available since 9.5 | Edit the workflows that Elastic provides. |
When you edit a workflow that runs as a service account, subsequent runs continue to use that account's privileges. Your changes can therefore use privileges you don't personally have. Grant workflow edit access only to users you trust to use those privileges.Adding, changing, or removing a service account assignment, and editing or deleting a workflow assigned to a service account, also require the `manage_security` cluster privilege. For account assignment instructions and required privileges, refer to [Run a workflow as a service account](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/explore-analyze/workflows/authoring-techniques/run-workflow-as-service-account).
## Privileges in the Management group
Each of the following privileges controls access to a different feature.
| Privilege | What it allows |
|----------------------------------------------------------------------------------------------------|--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Streams** Elastic Stack: Generally available since 9.1 | Access [Streams](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/solutions/observability/streams/streams), and change stream processing, retention, and routing. Elastic Stack: Generally available in 9.1 This privilege is in the **Observability** group. |
| **AI Anonymization** Elastic Stack: Generally available since 9.4 | Change the anonymization rules that control which field values are masked before they're sent to a large language model. |
| **Dev Tools** | Access [Console](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/explore-analyze/query-filter/tools/console), Search Profiler, and Grok Debugger. Users also need the matching Elasticsearch cluster and index privileges for the requests they run. |
| **Advanced Settings** | Change the settings that control how Kibana behaves in a space, such as the default index pattern and date format. |
| **Data View Management** | Create and edit [data views](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/explore-analyze/find-and-organize/data-views). |
| **Files Management** | Manage the files that other features store in Kibana. |
| **Shared images** | Upload and manage the images that other features reuse, such as dashboard panel images. |
| **Saved Objects Management** | Manage [saved objects](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/explore-analyze/find-and-organize/saved-objects), including importing, exporting, and copying them between spaces. |
| **Saved Query Management** | Save and manage [queries](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/explore-analyze/query-filter/tools/saved-queries) across all features that use them. |
| **Tag Management** | Create and edit [tags](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/explore-analyze/find-and-organize/tags), and apply them to saved objects. |
| **Stack Rules** | Create and manage [Elastic Stack rules](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/explore-analyze/alerting), such as index threshold and Elasticsearch query rules. |
| **Stack Alerts** Elastic Stack: Generally available since 9.5 | View and manage the alerts that Elastic Stack rules generate, without granting access to the rules themselves. |
| **Osquery** | Access [Osquery](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/solutions/security/investigate/osquery), and run and save queries. Turn on **Customize sub-feature privileges** to grant individual Osquery privileges. For the full list, refer to [Osquery sub-feature privileges](#kibana-privileges-osquery-subfeatures). |
| **Actions and Connectors** | Create and manage [connectors](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/deploy-manage/manage-connectors), and run the actions that rules and cases trigger. Turn on **Customize sub-feature privileges** to grant the endpoint security privilege. For details, refer to [Actions and Connectors sub-feature privileges](#kibana-privileges-actions-subfeatures). |
| **Cases** | Access [cases](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/explore-analyze/cases), and create and edit them. Turn on **Customize sub-feature privileges** to grant individual case privileges. For the full list, refer to [Customize sub-feature privileges for cases](/elastic/docs-content/pull/8921/explore-analyze/cases/control-case-access#cases-sub-feature-privileges). |
| **Inference Endpoints** | Create and manage [inference endpoints](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/explore-analyze/elastic-inference/inference-api). Elastic Stack: Generally available from 9.0 to 9.3 This privilege is in the **Elasticsearch** group. |
| **Cloud Connect** Elastic Stack: Generally available since 9.3 | Connect a cluster to Elastic Cloud services. This privilege appears on Elastic Cloud Enterprise and self-managed clusters, but not on Elastic Cloud Hosted. |
| **Automatic Import** Elastic Stack: Generally available since 9.4 | Access [Automatic Import](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/solutions/security/get-started/automatic-import), and create custom integrations from sample data. |
| **Data Set Quality** | Access the [Data Set Quality](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/solutions/observability/data-set-quality-monitoring) page. Turn on **Customize sub-feature privileges** to grant individual data set quality privileges. For the full list, refer to [Data Set Quality sub-feature privileges](#kibana-privileges-data-set-quality-subfeatures). |
| **Fleet** | Access [Fleet](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/reference/fleet), and manage agents and agent policies. Turn on **Customize sub-feature privileges** to grant individual Fleet privileges. For the full list, refer to [Fleet privileges and available actions](/elastic/docs-content/pull/8921/reference/fleet/fleet-roles-privileges#fleet-roles-and-privileges-sub-features-table). |
| **Integrations** | Browse and install [integrations](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/reference/fleet). |
| **Maintenance Windows** | Create and manage [maintenance windows](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/explore-analyze/alerting/alerts/maintenance-windows), which suppress rule notifications for a scheduled period. |
| **Manage Scheduled Reports** Elastic Stack: Generally available since 9.1 | View and manage the [scheduled reports](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/explore-analyze/report-and-share/automating-report-generation) of every user in the space. |
| **Query activity** Elastic Stack: Generally available since 9.4 | Access [Query activity](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/deploy-manage/monitor/query-activity), and cancel long-running queries. |
| **Rules Settings** | Change the settings that apply to all rules in a space. Turn on **Customize sub-feature privileges** to grant individual rule settings privileges. For the full list, refer to [Rules Settings sub-feature privileges](#kibana-privileges-rules-settings-subfeatures). |
| **Stack Monitoring** | Access [Elastic Stack monitoring](https://docs-v3-preview.elastic.dev/elastic/docs-content/pull/8921/deploy-manage/monitor/stack-monitoring). This privilege has no access levels to select: to grant access, assign the `monitoring_user` role. |
| **AI Assistant** Elastic Stack: Removed in 9.3 | Change which AI Assistants are available, from the AI Assistant settings in Elastic Stack Management. Elastic Stack: Generally available in 9.2 This privilege is called **AI Assistant Settings**. |
| **Setup guides** Elastic Stack: Removed in 9.2 | Access the getting-started page that helps you ingest data and start using Search, Observability, or Security. |
| **Entity Manager** Elastic Stack: Removed in 9.1 | Access the Elastic Entity Model of hosts, containers, and services in Observability. |
### Osquery sub-feature privileges
These privileges control specific parts of Osquery. Selecting **All** includes everything in the following table.
| Privilege | What it allows |
|-------------------|------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------|
| **Live queries** | Run live queries against hosts, and view the results. **Read** allows viewing the results of queries that other users ran. Select **Run Saved queries** within this privilege to also allow running saved queries without being able to change them. |
| **Saved queries** | Create, edit, and delete saved queries. |
| **Packs** | Create, edit, and delete query packs, and schedule them to run against agent policies. |
### Actions and Connectors sub-feature privileges
This privilege controls a specific action on connectors. Selecting **All** includes everything in the following table.
| Privilege | What it allows |
|-------------|--------------------------------------------------------------------------------------------------------------------|
| **Execute** | Run the endpoint security connectors, which include SentinelOne, CrowdStrike, and Microsoft Defender for Endpoint. |
### Data Set Quality sub-feature privileges
- Elastic Stack: Generally available since 9.1
These privileges control specific actions on the **Data Set Quality** page. Selecting **All** includes everything in the following table.
| Privilege | What it allows |
|-------------------|-------------------------------------------------------------|
| **Manage rules** | Create and edit the rules that alert on degraded documents. |
| **Manage alerts** | View and manage the alerts that those rules generate. |
### Rules Settings sub-feature privileges
These privileges control the settings that apply to all rules in a space. Selecting **All** includes everything in the following table.
| Privilege | What it allows |
|------------------------------------------------------------------------------------------|---------------------------------------------------------------------------------------|
| **Flapping detection** | Change the settings that control when an alert is treated as flapping between states. |
| **Alert deletion** Elastic Stack: Generally available since 9.1 | Change how long alerts are kept before they're deleted, and delete them on demand. |