Role management using Kibana
Roles are a collection of privileges that allow you to perform actions in Kibana and Elasticsearch. Users are not directly granted privileges, but are instead assigned one or more roles that describe the desired level of access. When you assign a user multiple roles, the user receives a union of the roles’ privileges. This means that you cannot reduce the privileges of a user by assigning them an additional role. You must instead remove or edit one of their existing roles.
To create a role:
- Go to the Roles management page in the navigation menu or use the global search field.
- Click Create role.
The manage_security cluster privilege is required to access role management.
Cluster privileges grant access to monitoring and management features in Elasticsearch. They also enable Stack Management capabilities in Kibana.
Refer to cluster privileges for a complete description of available options.
Each role can grant access to multiple data indices, and each index can have a different set of privileges. We recommend granting the read and view_index_metadata privileges to each index that you expect your users to work with in Kibana.
Refer to index privileges for a complete description of available options.
Document-level and field-level security affords you even more granularity when it comes to granting access to your data. With document-level security (DLS), you can write an Elasticsearch query to describe which documents this role grants access to. With field-level security (FLS), you can instruct Elasticsearch to grant or deny access to specific fields within each document.
Go to the Roles management page in the navigation menu or use the global search field.
Click Create role.
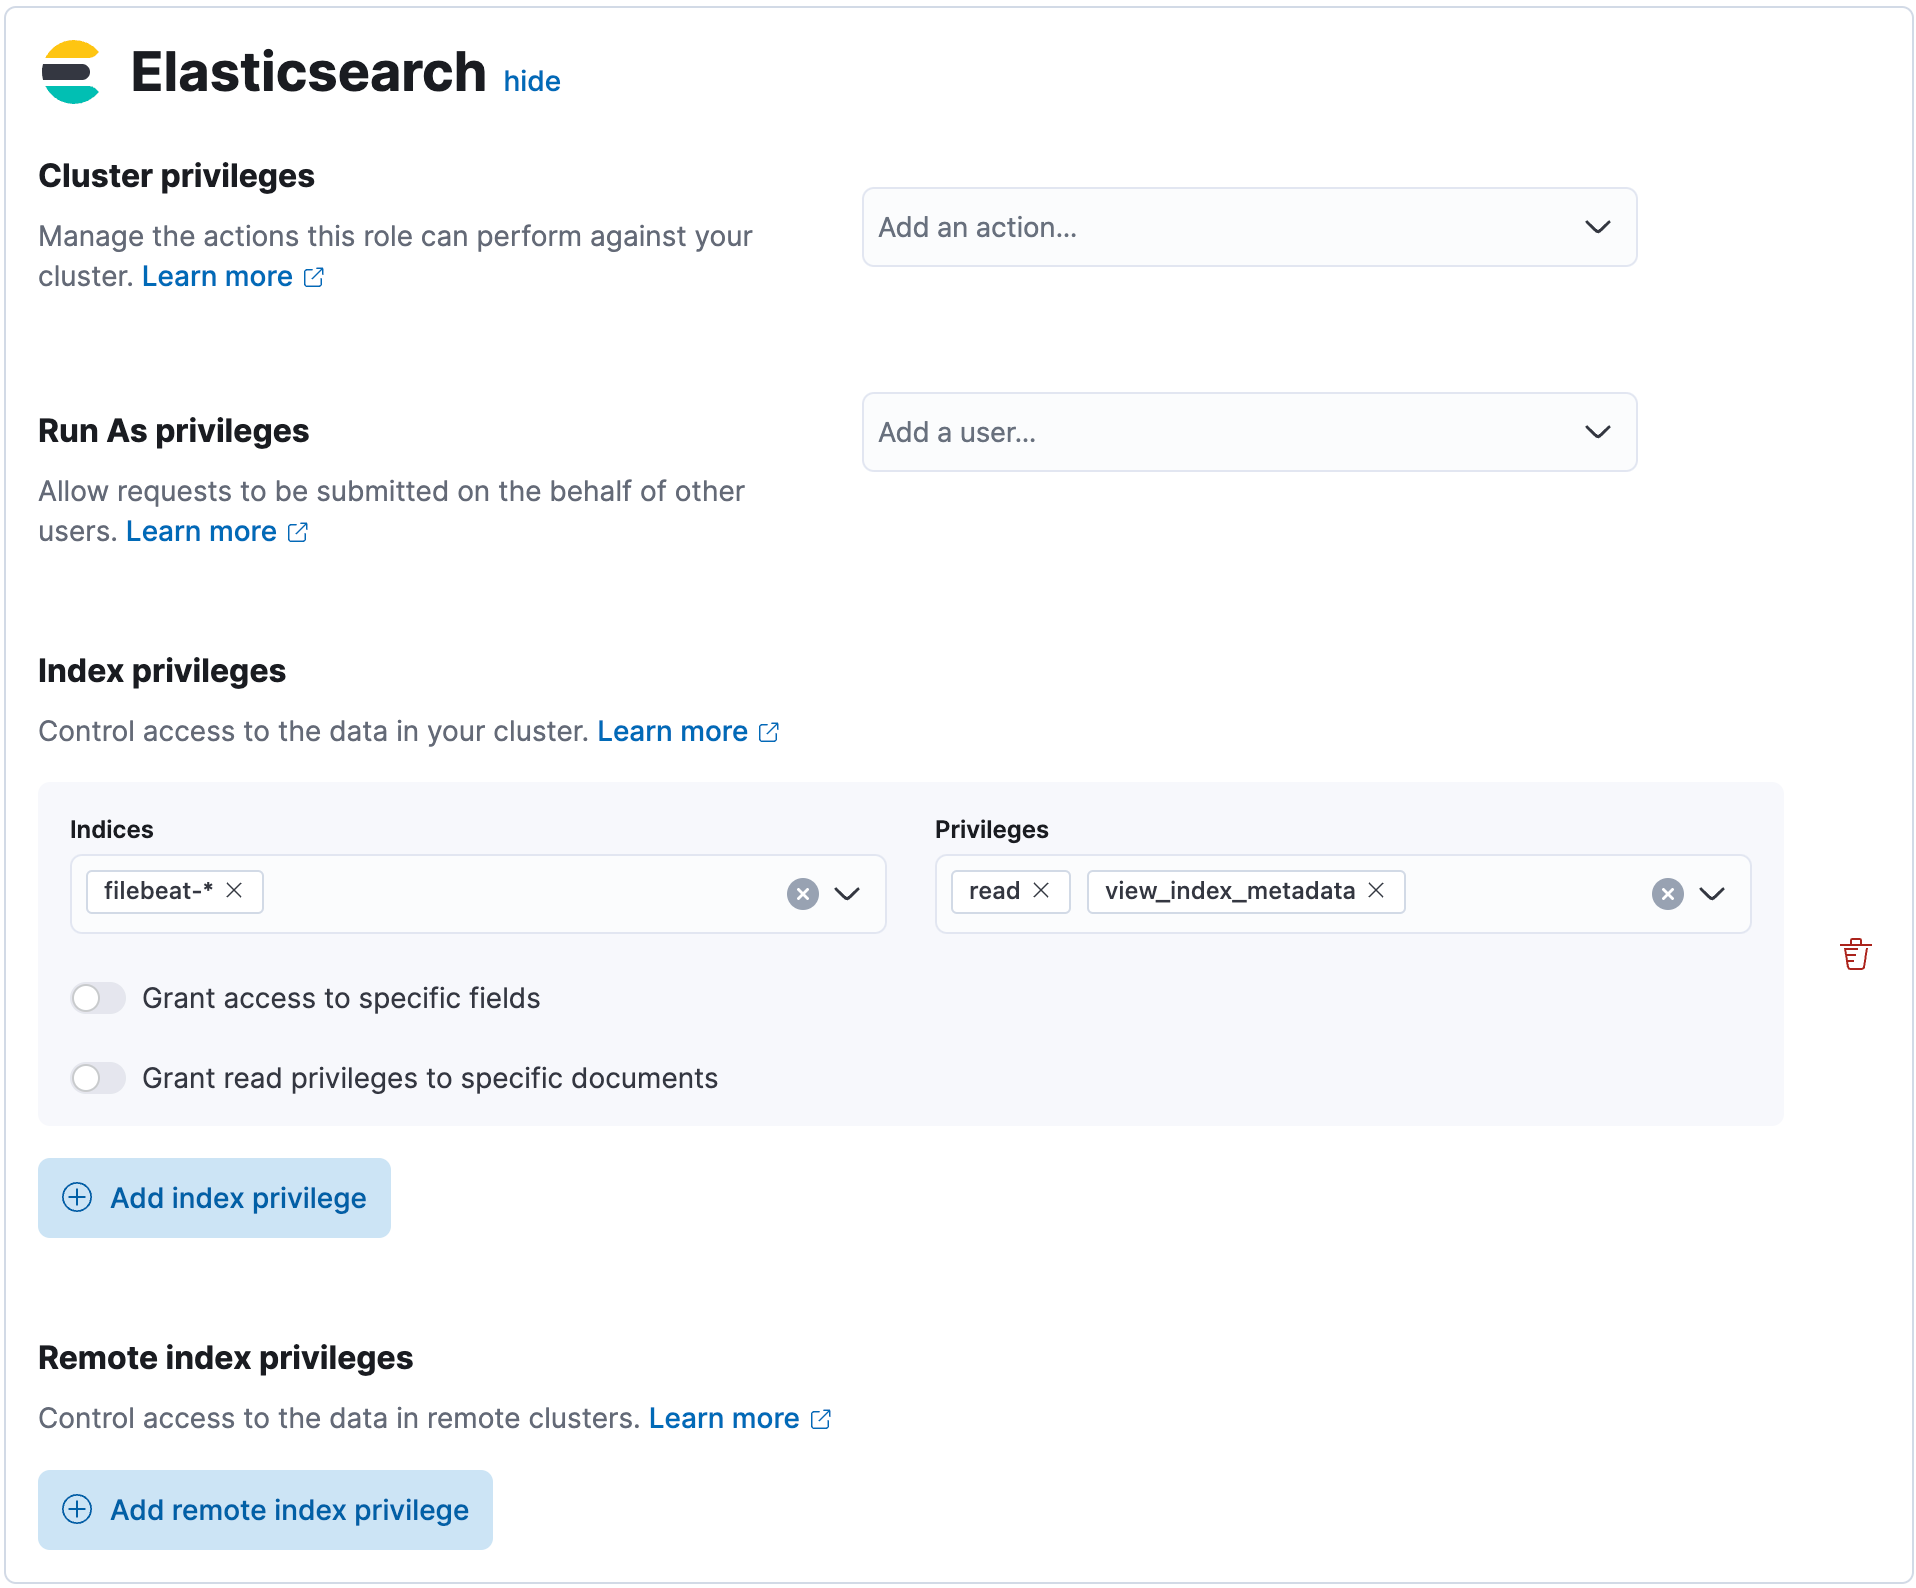
In Index privileges, enter:
filebeat-*in the Index field.readandview_index_metadatain the Privileges field.
Document-level security is a subscription feature.
Go to the Roles management page in the navigation menu or use the global search field.
Click Create role.
In Index privileges, enter:
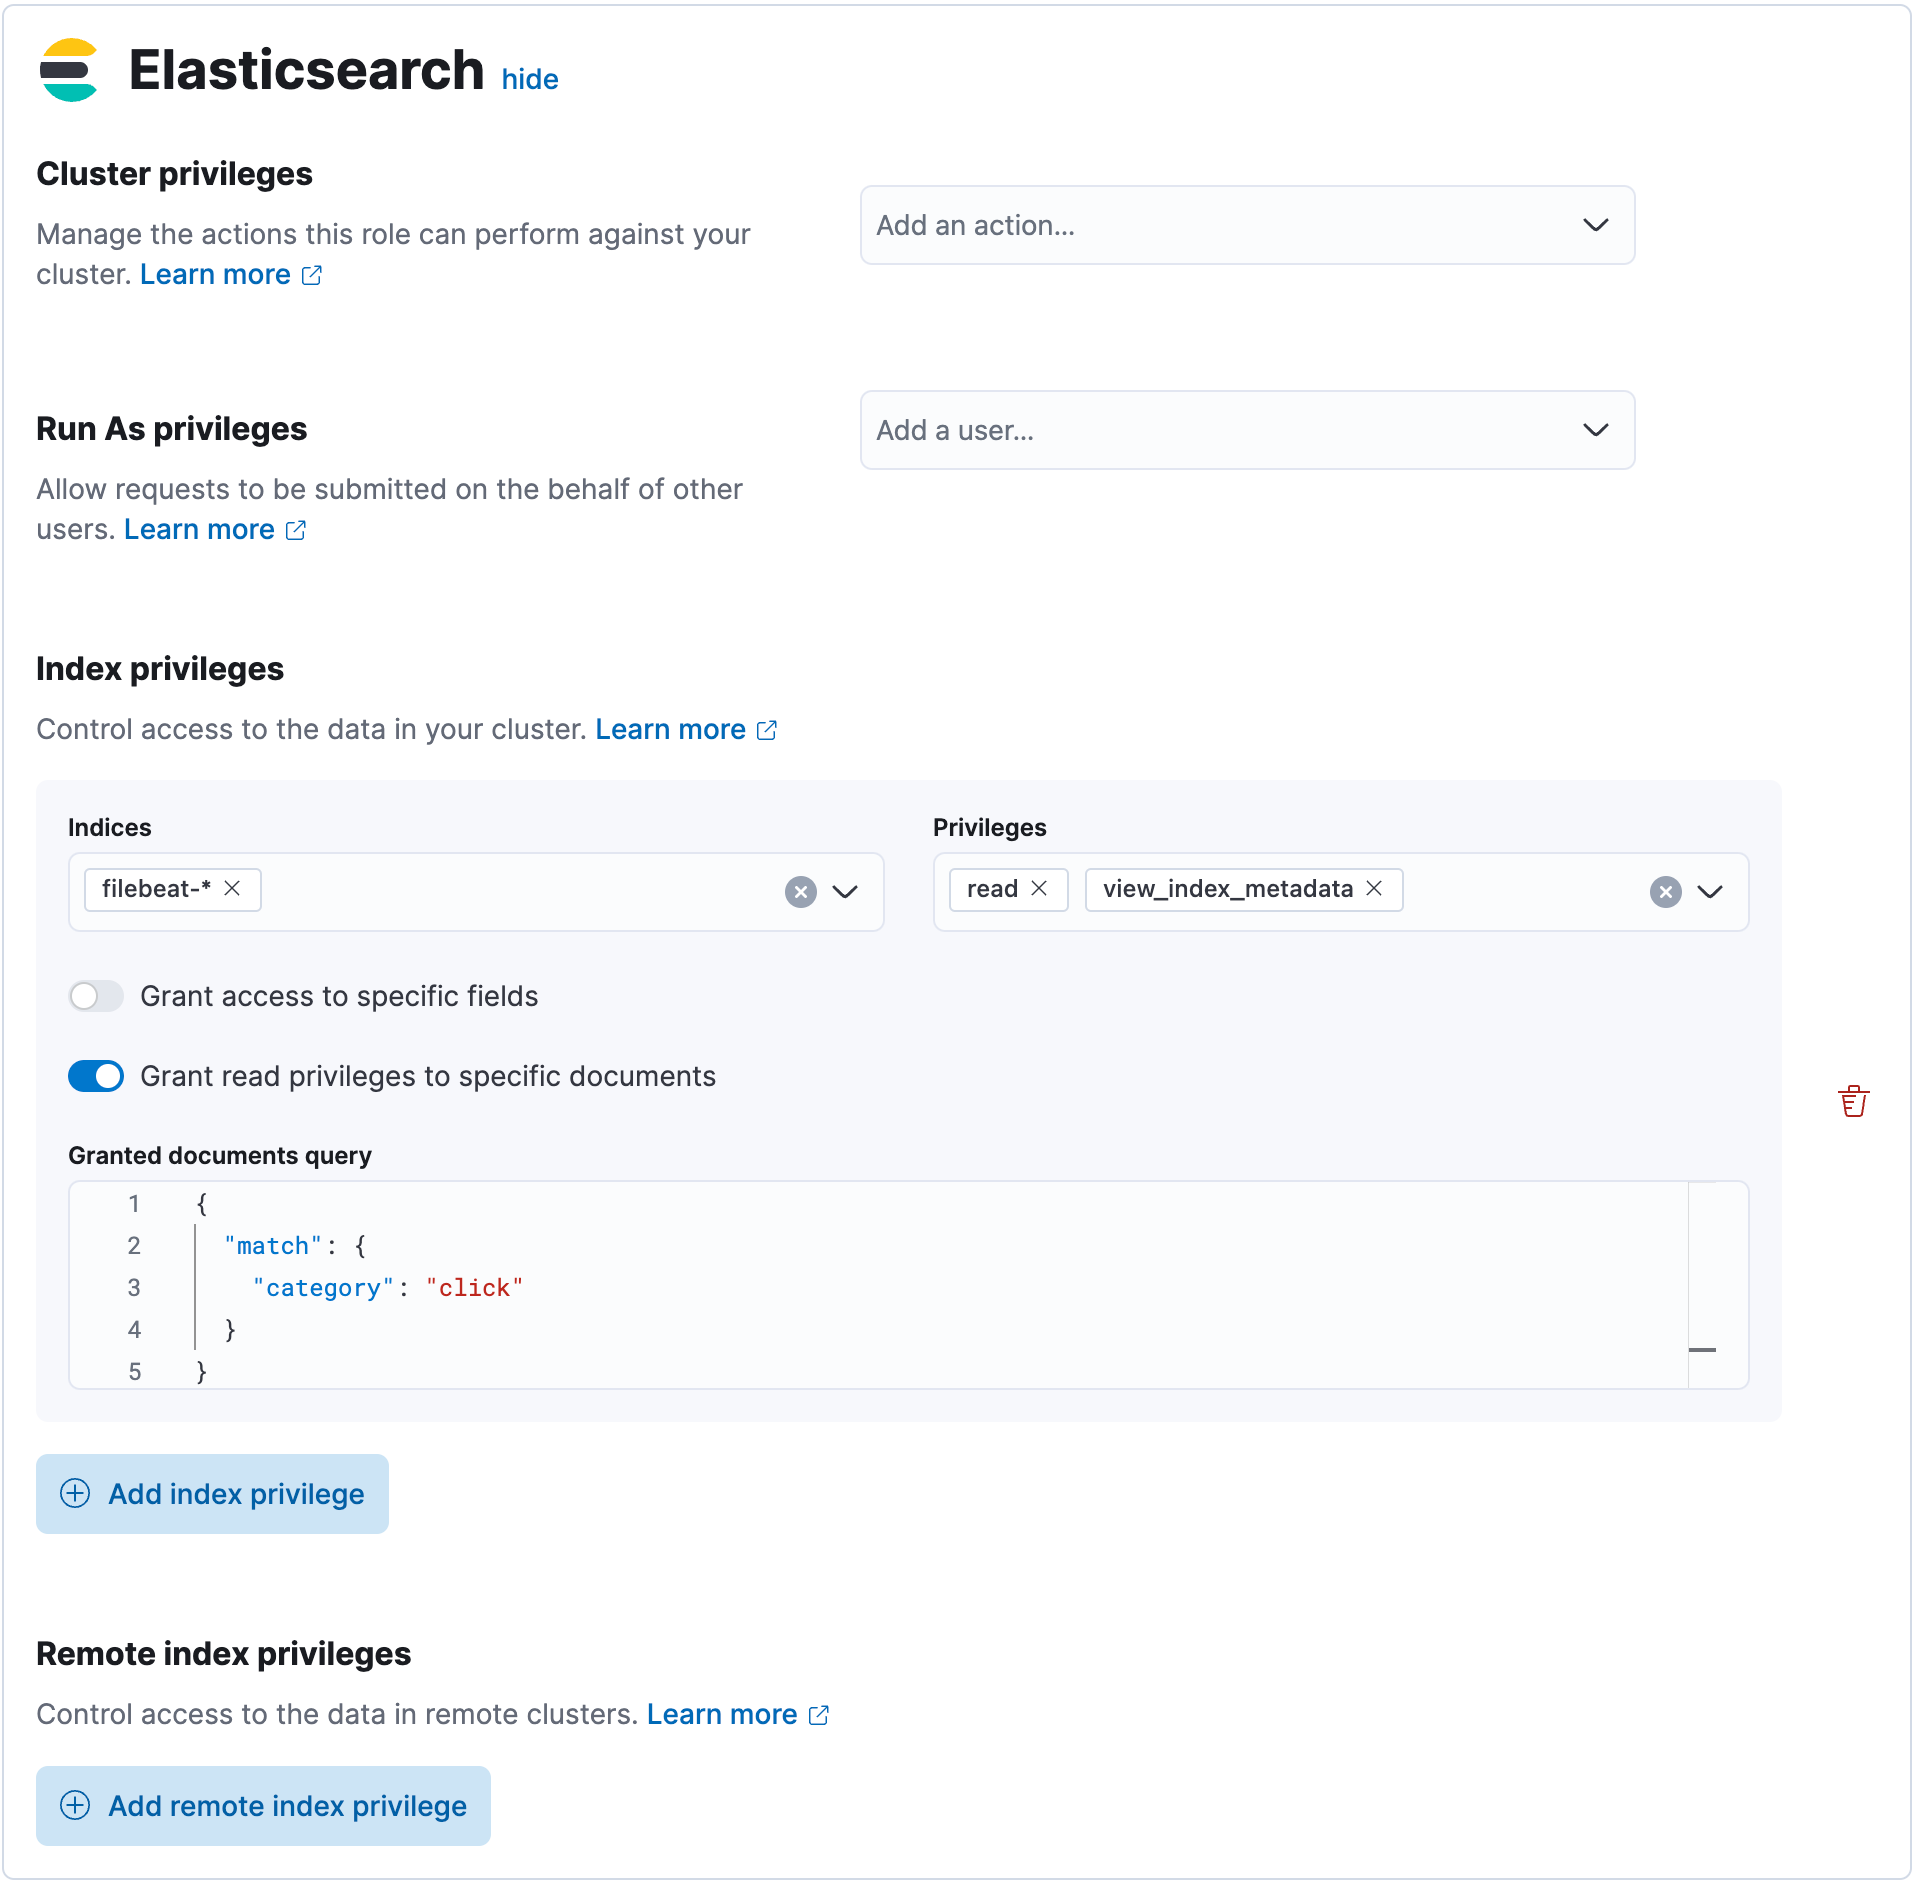
filebeat-*in the Indices field.readandview_index_metadatain the Privileges field.
Select Grant read privileges to specific documents.
Enter an Elasticsearch query that matches the documents your users should access. This example writes a query that allows access to documents that have a
categoryfield equal toclick:{ "match": { "category": "click" } }NoteKibana automatically surrounds your DLS query with a
queryblock, so you don’t have to provide your own.
If you have at least a platinum license, you can manage access to indices in remote clusters.
You can assign the same privileges, document-level, and field-level as for local index privileges.
Go to the Roles management page in the navigation menu or use the global search field.
Click Create role.
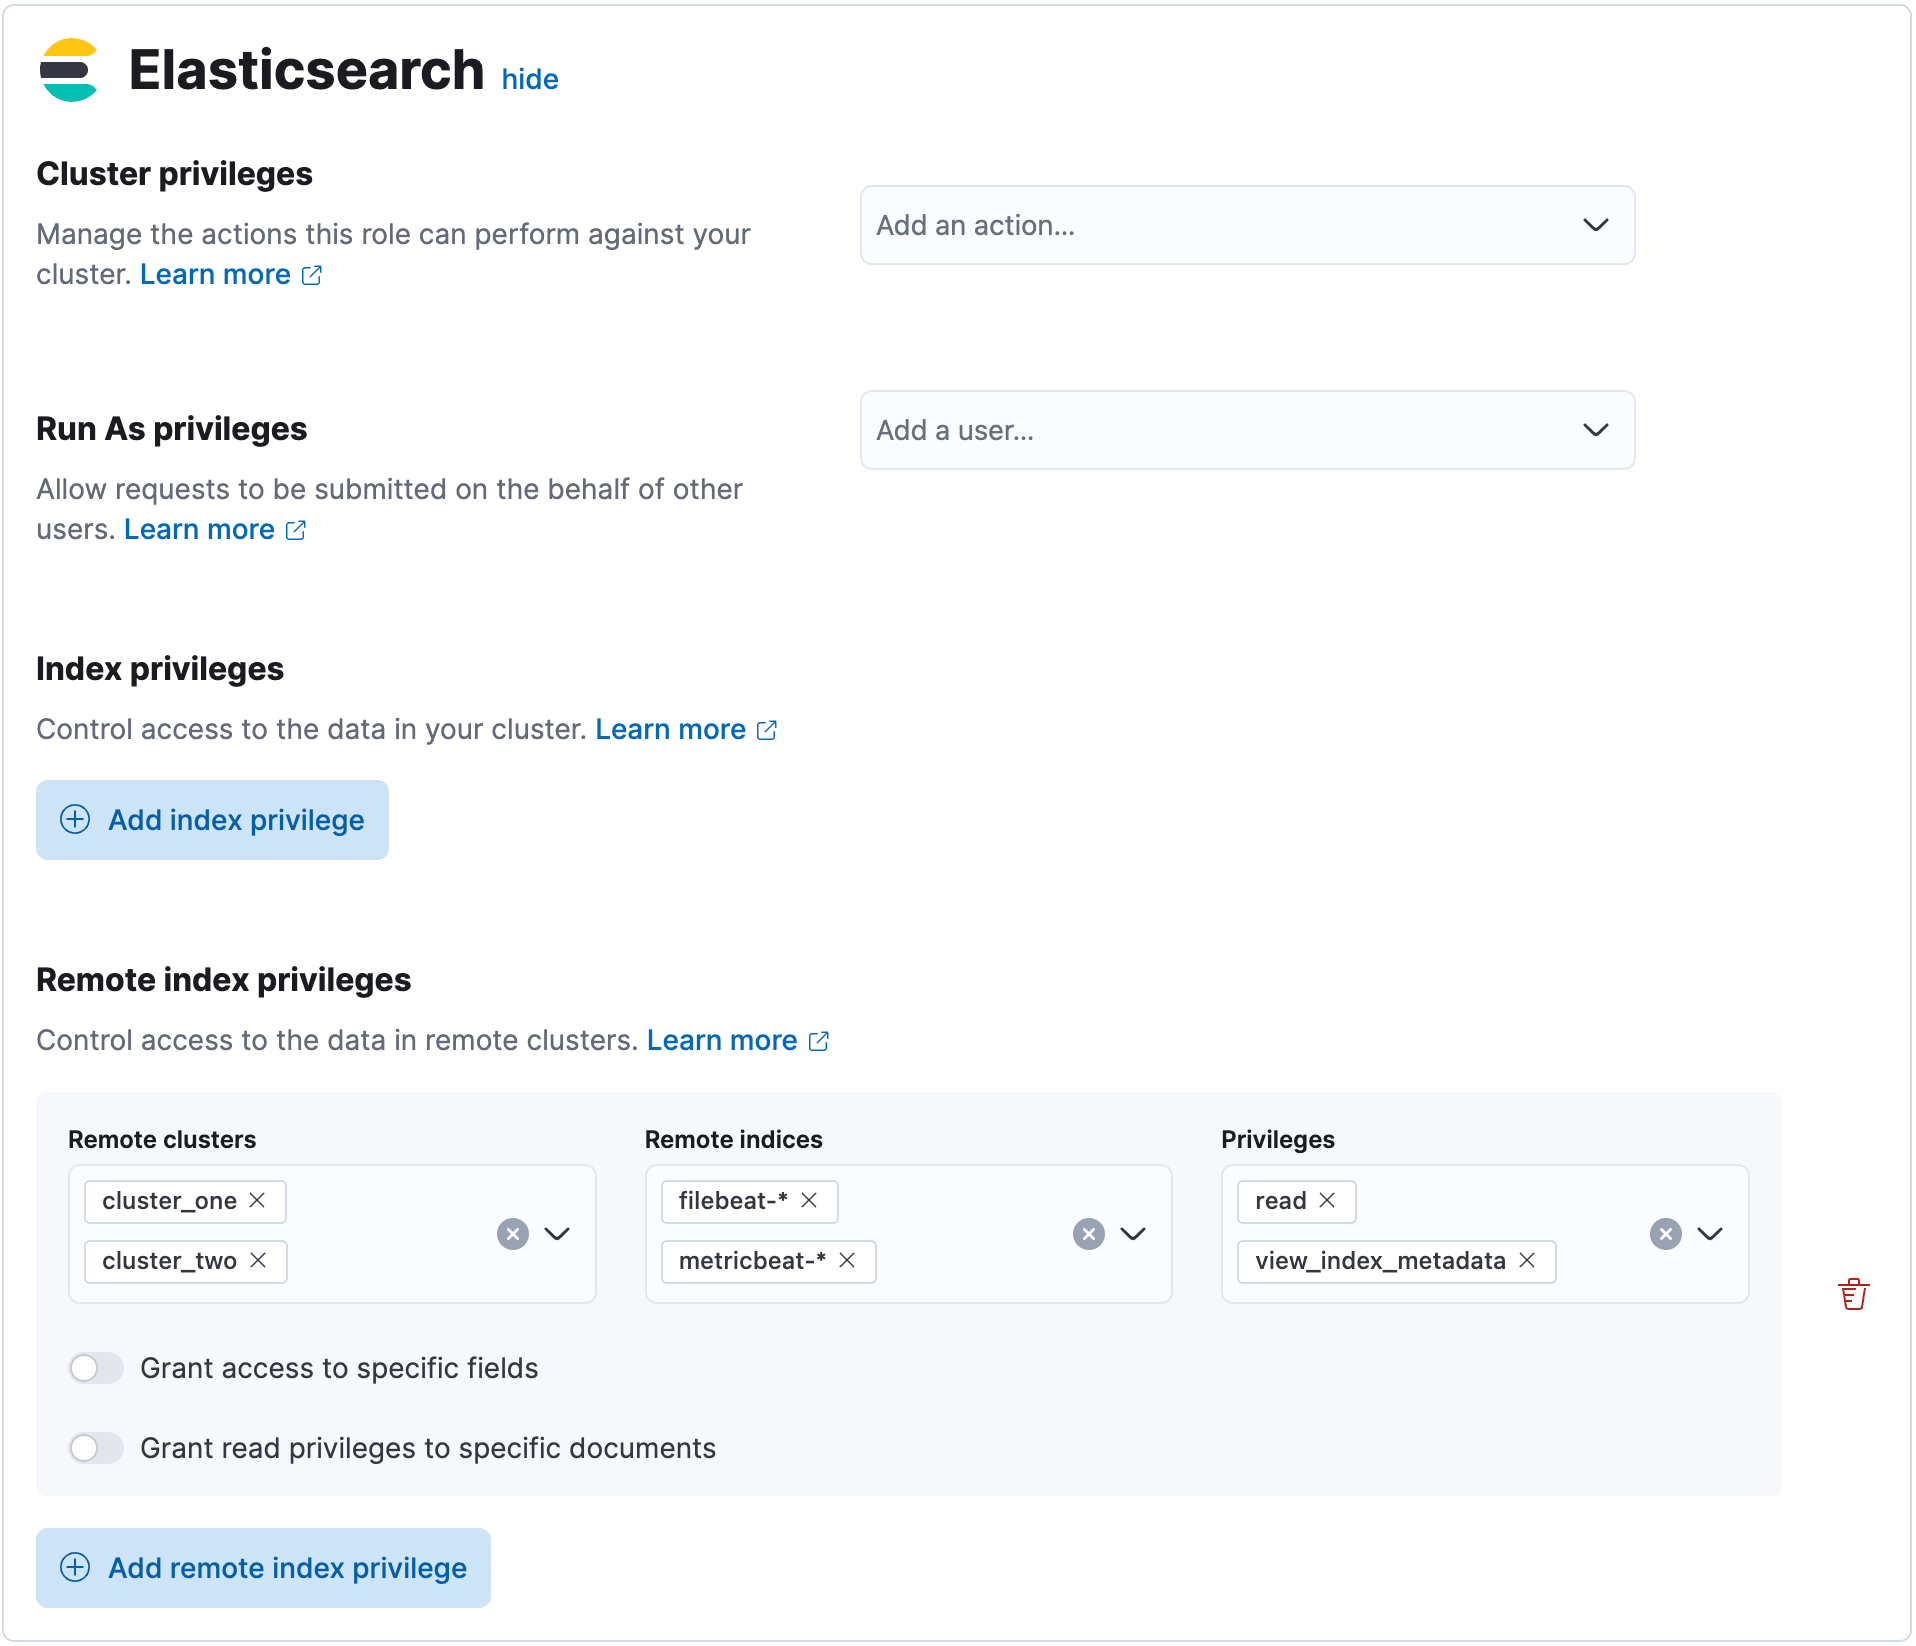
In Remote index privileges, enter:
- The name of your remote cluster in the Remote clusters field.
- The name of the index in your remote cluster in the Remote indices field.
- The allowed actions in the Privileges field. (e.g.
readandview_index_metadata)
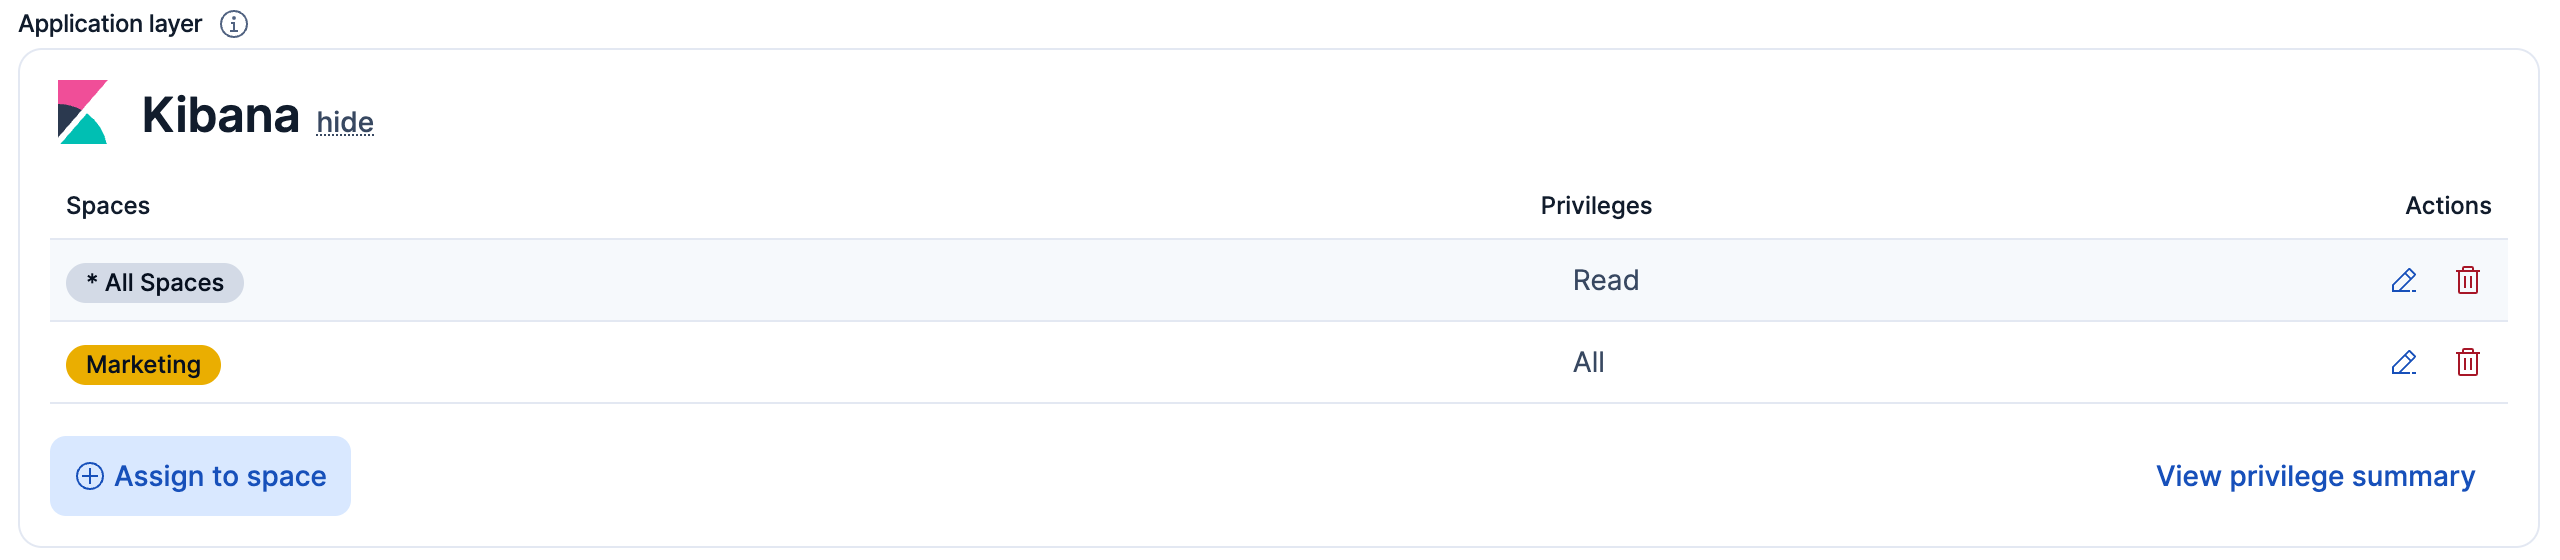
To assign Kibana privileges to the role, click Assign to space in the Kibana section.
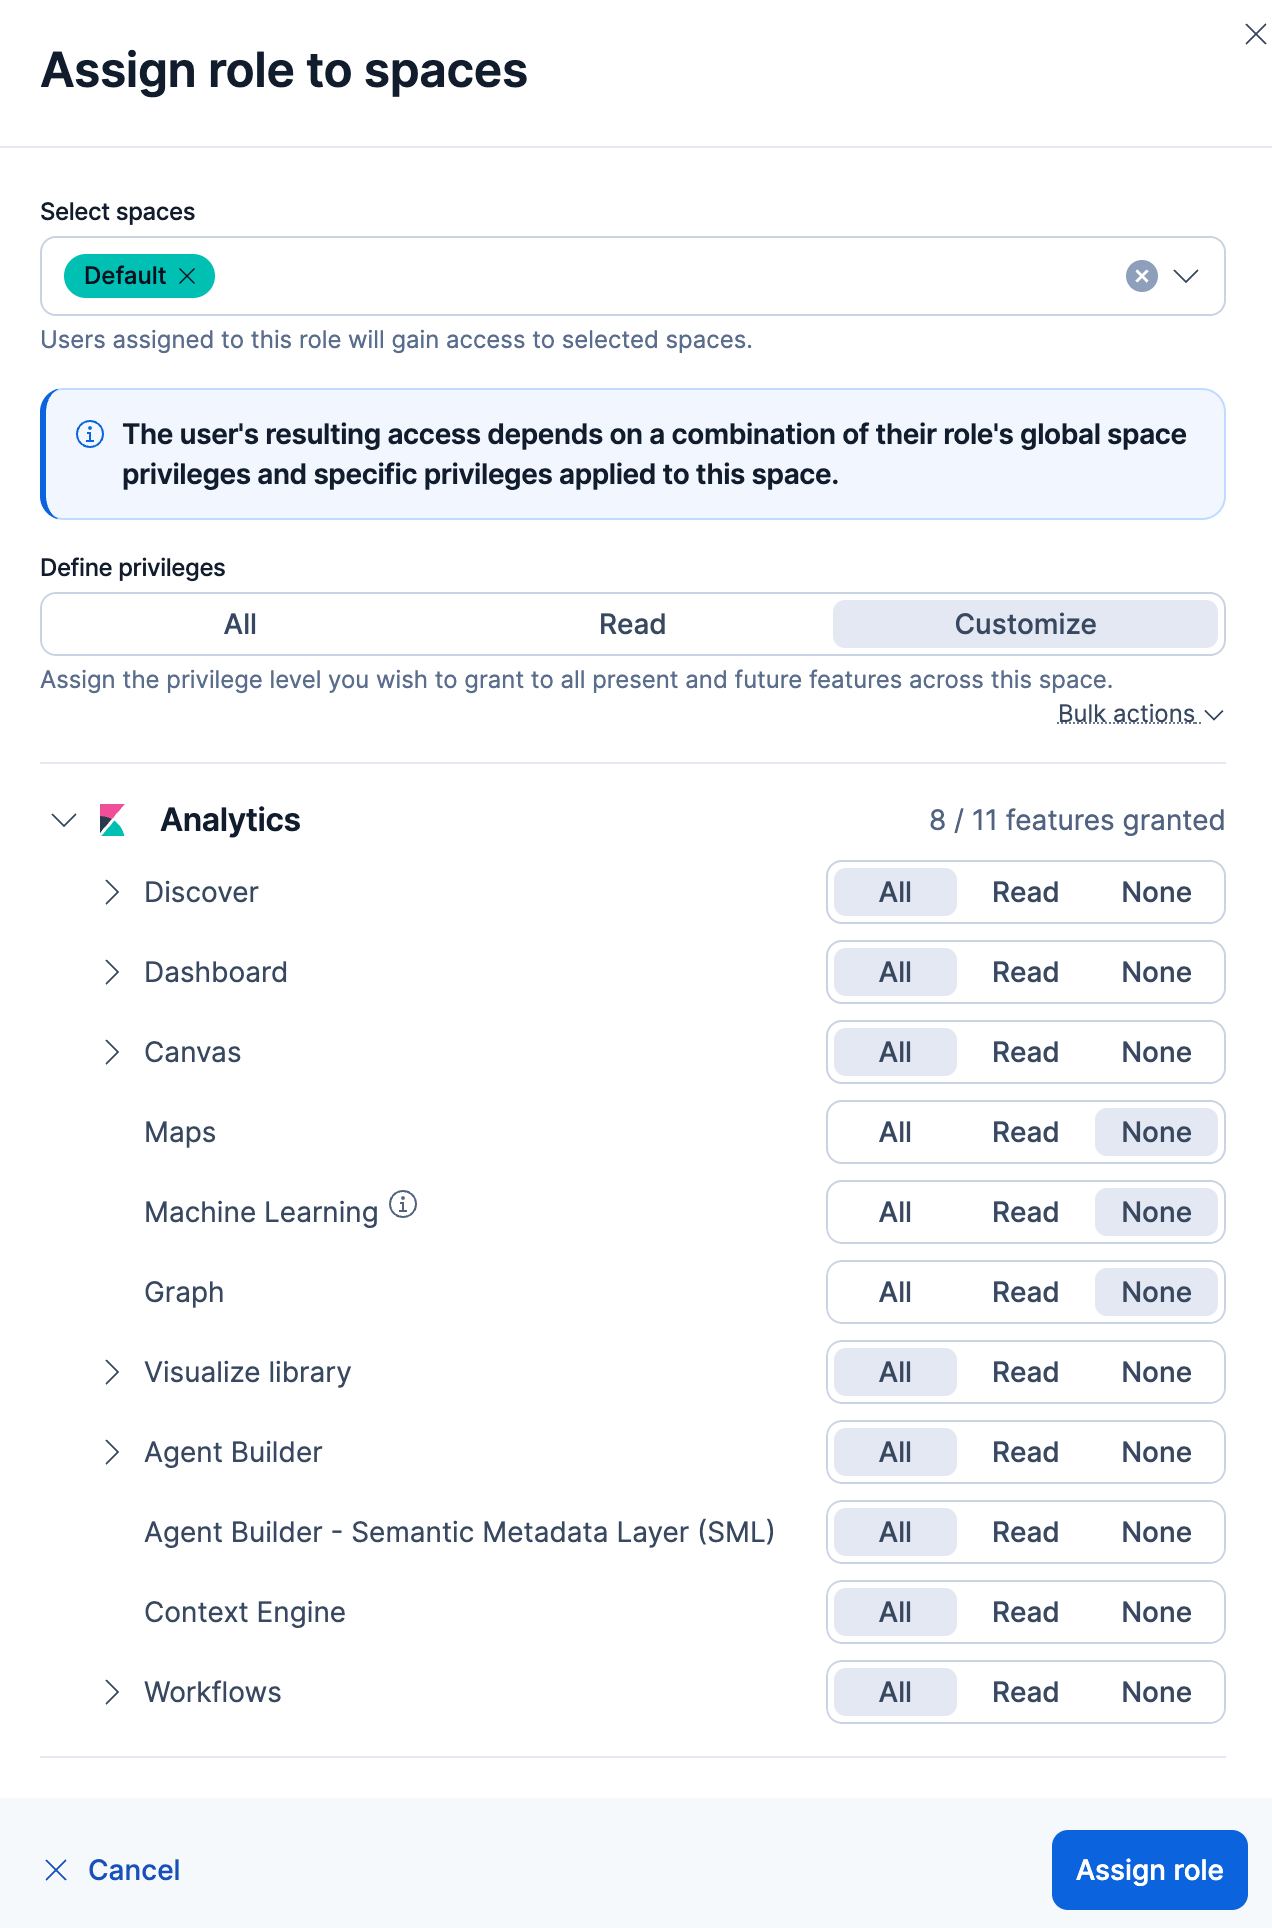
Open the Select spaces field to specify whether to grant the role access to all spaces All Spaces or one or more individual spaces. If you select All Spaces, you can’t select individual spaces until you clear your selection.
Use Define privileges to grant access to features. The default is Customize, which you can use to grant access to individual features. Otherwise, you can grant read and write access to all current and future features by selecting All, or grant read access to all current and future features by selecting Read.
When you select Customize, you can choose either All, Read or None for access to each feature. As new features are added to Kibana, roles that use the Customize option do not automatically get access to the new features. You must manually update the roles.
Stack Monitoring relies on built-in roles to grant access. When a user is assigned the appropriate roles, the Stack Monitoring application is available; otherwise, it is not visible.
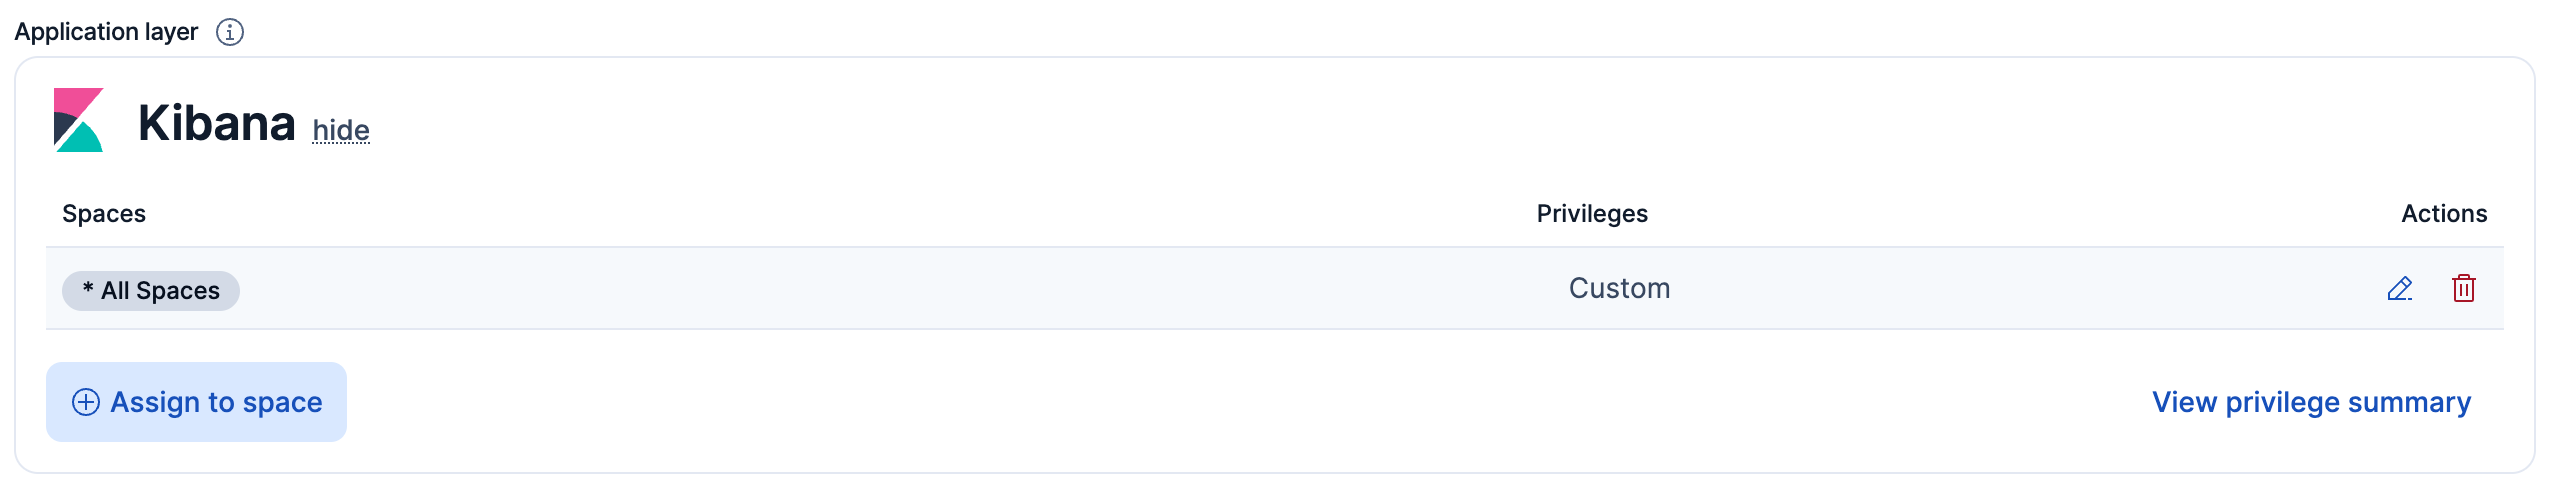
To apply your changes, click Assign role. The privilege shows up under the Kibana privileges section of the role.
Features are available to users when their roles grant access to the features, and those features are visible in their current space. The following matrix explains when features are available to users when controlling access via spaces and role-based access control:
| Spaces config | Role config | Result |
|---|---|---|
| Feature hidden | Feature disabled | Feature not available |
| Feature hidden | Feature enabled | Feature not available |
| Feature visible | Feature disabled | Feature not available |
| Feature visible | Feature enabled | Feature available |
Using the same role, it’s possible to assign different privileges to different spaces. After you’ve added privileges, click Assign to space. If you’ve already added privileges for either All Spaces or an individual space, you will not be able to select these in the Select spaces field.
Additionally, if you’ve already assigned privileges at All Spaces, you are only able to assign additional privileges to individual spaces. Similar to the behavior of multiple roles granting the union of all privileges, Kibana privileges are also a union. If you’ve already granted the user the All privilege at All Spaces, you’re not able to restrict the role to only the Read privilege at an individual space.
To view a summary of the privileges granted, click View privilege summary.
- Click Assign to space.
- In the Select spaces field, select an individual space.
- For Define privileges, leave the default selection of Customize.
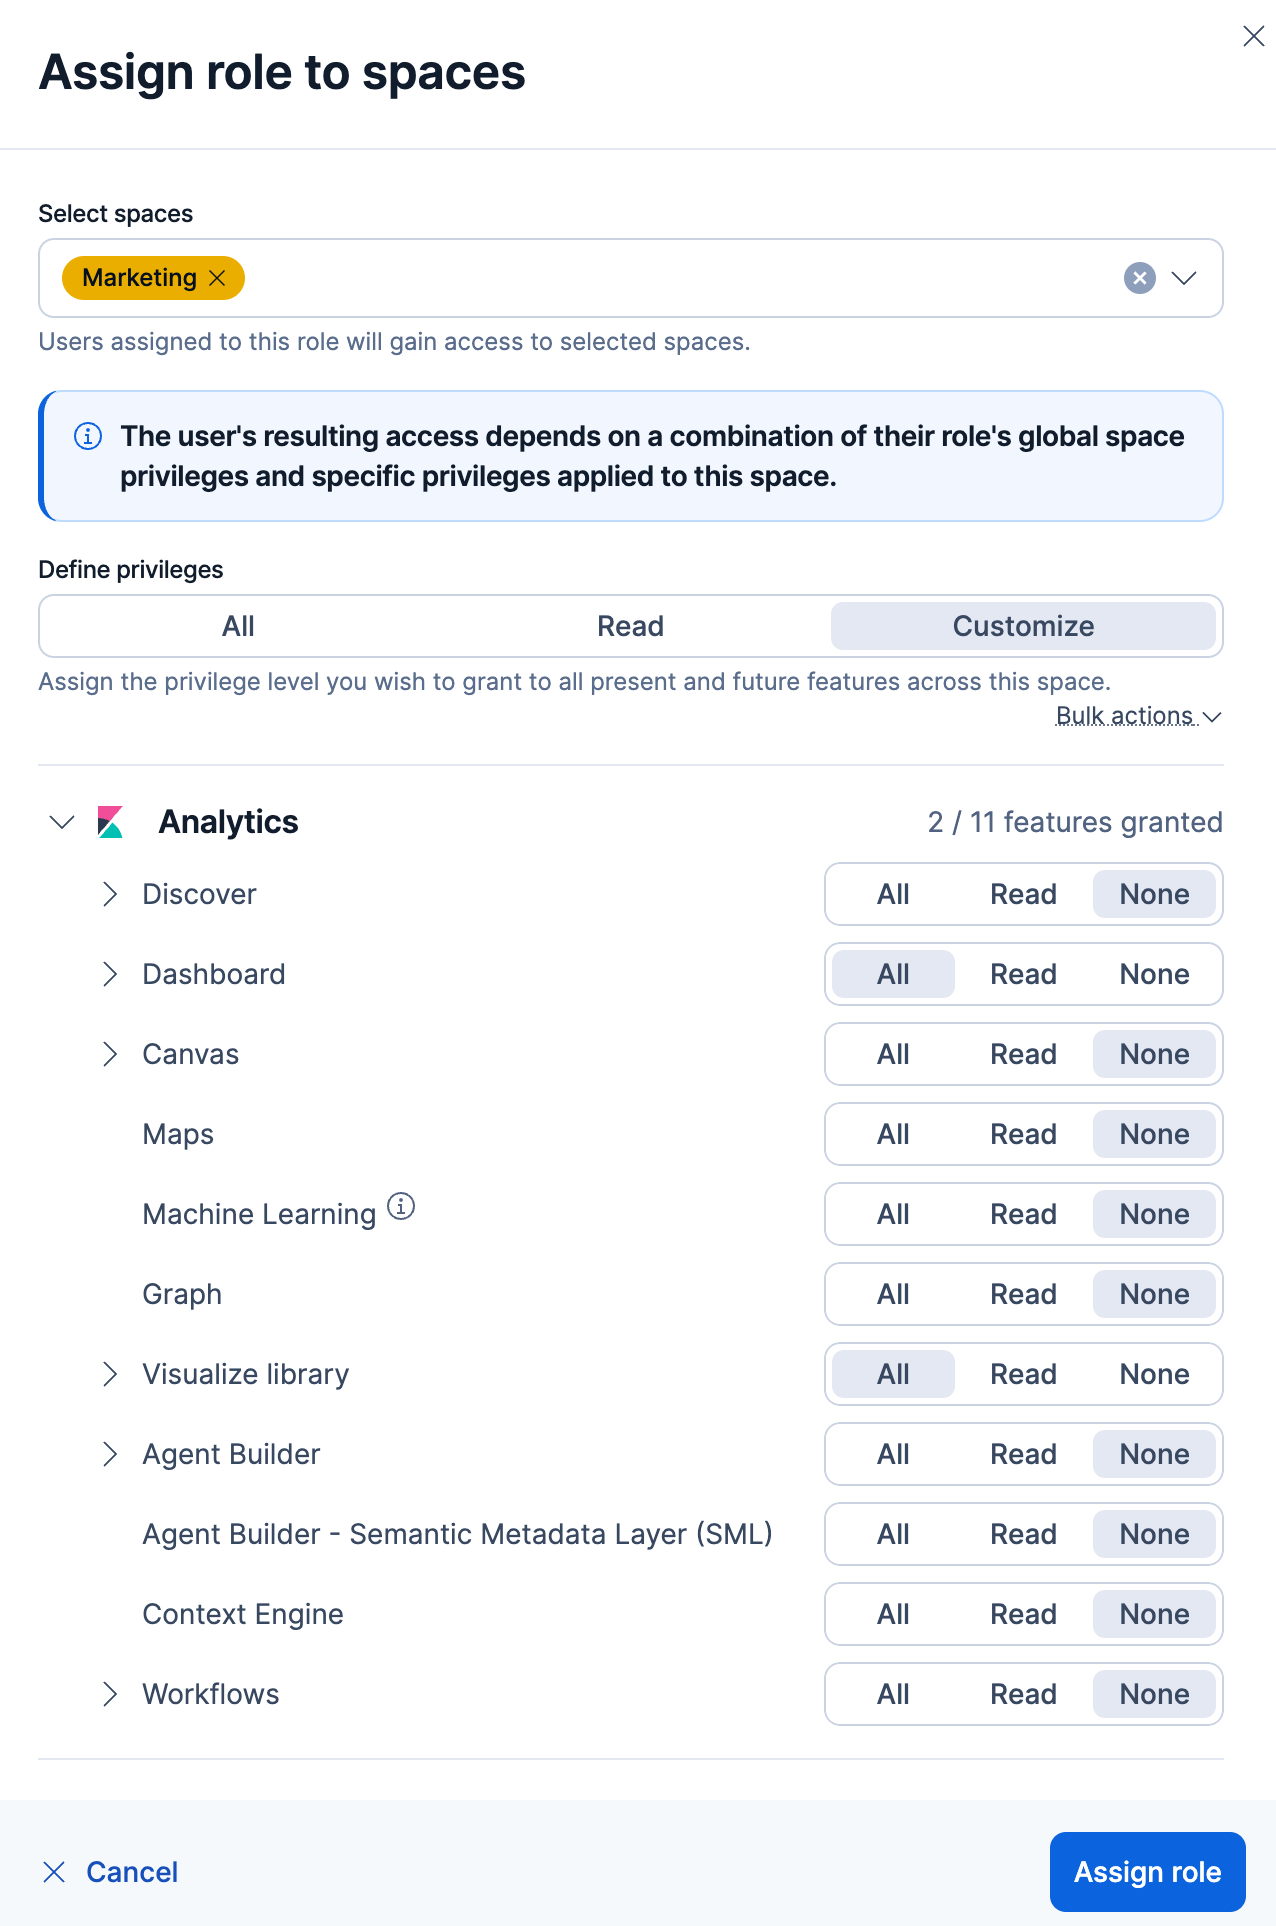
- For the Dashboard and Visualize library features, select All. Dashboard alone gives read-only access to the visualizations on a dashboard, so Visualize library lets users create and edit them.
- Click Assign role.
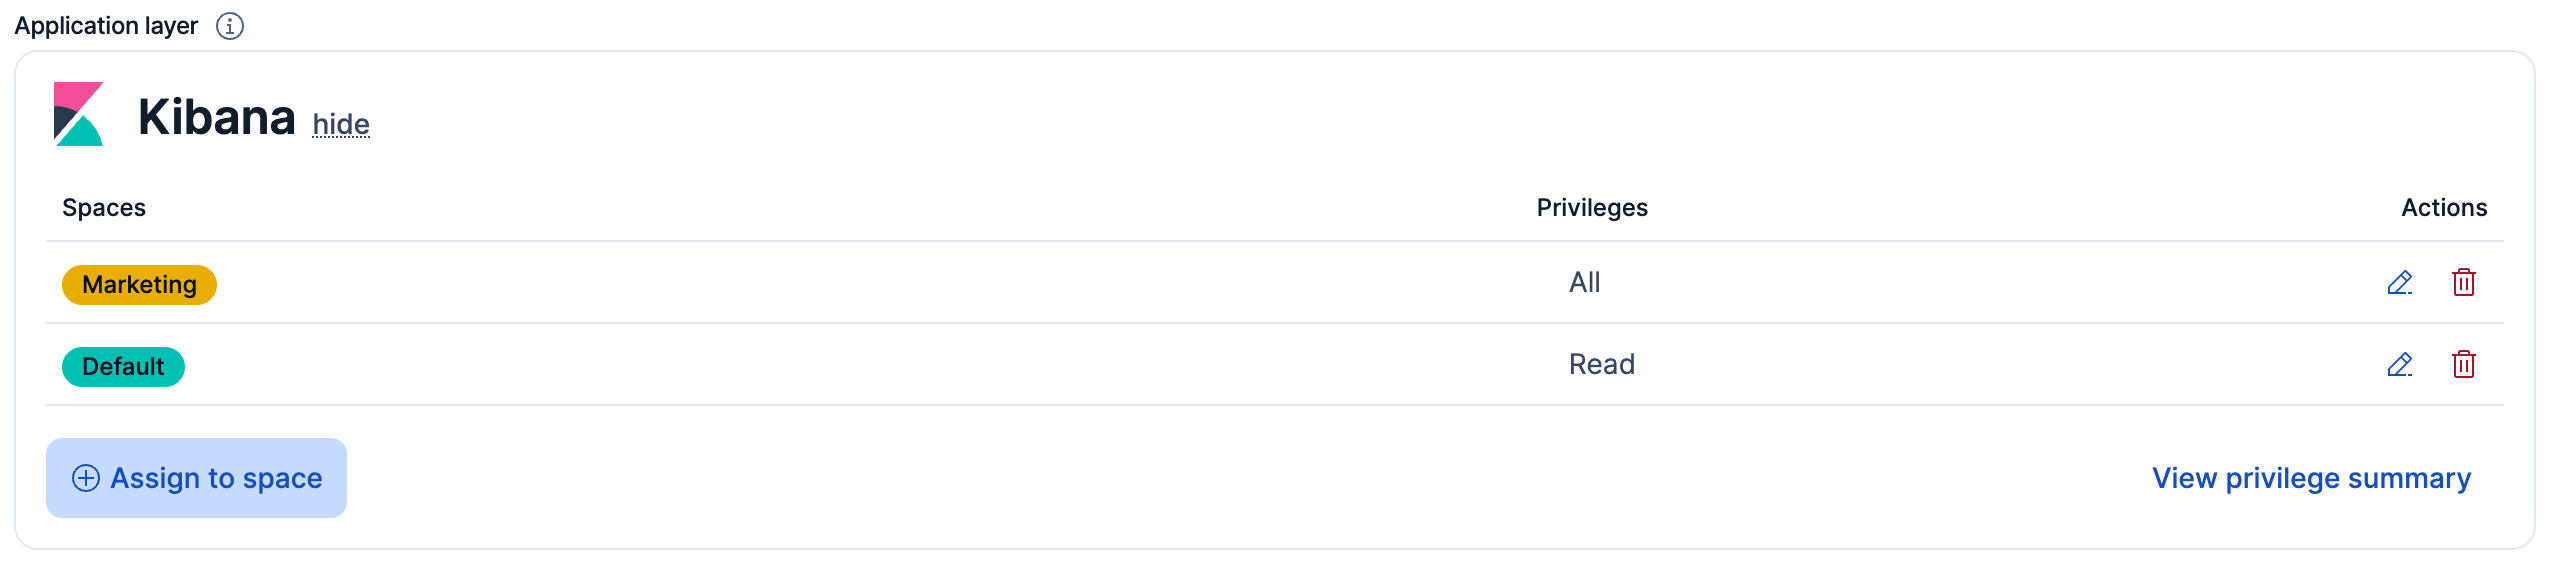
- Click Assign to space.
- In the Select spaces field, select the first space.
- For Define privileges, select All.
- Click Assign role.
- Click Assign to space.
- In the Select spaces field, select the second space.
- For Define privileges, select Read.
- Click Assign role.
- Click Assign to space.
- In the Select spaces field, select All Spaces.
- For Define privileges, select Read.
- Click Assign role.
- Click Assign to space.
- In the Select spaces field, select the individual space.
- For Define privileges, select All.
- Click Assign role.